Remote work has transformed from a temporary pandemic measure into a permanent fixture of modern business operations. As organizations continue to support distributed teams across multiple locations and time zones, the need for secure, reliable remote access solutions has never been more critical. VPN access remote technologies serve as the backbone of this new work paradigm, enabling employees to connect safely to corporate resources from anywhere in the world while maintaining the security posture that businesses require.
Understanding VPN Access Remote Infrastructure
VPN access remote solutions create encrypted tunnels between remote endpoints and corporate networks, ensuring that sensitive data remains protected during transmission. This technology allows employees working from home offices, coffee shops, airports, or any location with internet connectivity to access internal business systems as if they were sitting at their office desk.
The fundamental architecture of vpn access remote systems involves several key components working in concert. Client software installed on employee devices initiates connection requests to VPN gateway servers positioned at the network perimeter. These gateways authenticate users, establish encrypted tunnels using protocols like OpenVPN, WireGuard, or IKEv2/IPsec, and route traffic between remote clients and internal resources.
Core Components of Remote Access Architecture
Modern vpn access remote deployments typically include:
- VPN client applications installed on laptops, smartphones, and tablets
- Authentication servers that verify user credentials and device compliance
- VPN concentrators or gateways that handle encryption and tunnel management
- Access control systems that enforce policy-based permissions
- Monitoring and logging infrastructure for security auditing
Organizations must carefully plan their remote access architecture to balance security requirements with user experience. Overloaded VPN gateways create bottlenecks that frustrate remote workers, while inadequate security controls expose the network to unauthorized access and data breaches.
Security Protocols for VPN Access Remote Solutions
The strength of any vpn access remote implementation depends heavily on the cryptographic protocols and security measures deployed. In 2026, legacy protocols like PPTP have long been deprecated due to known vulnerabilities, while modern alternatives provide robust protection against evolving threats.
Protocol Selection and Configuration
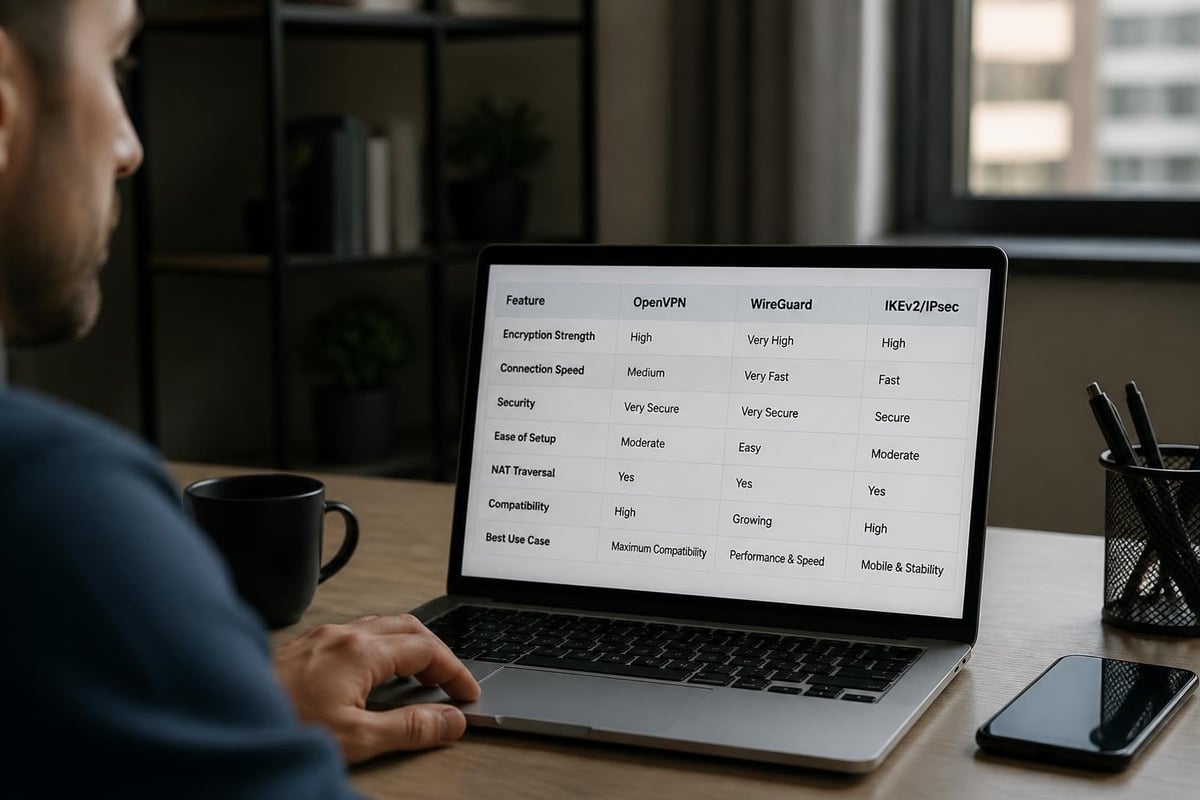
Organizations should prioritize protocols that offer strong encryption, perfect forward secrecy, and resistance to known attack vectors. WireGuard has gained significant adoption due to its lean codebase and excellent performance characteristics, while OpenVPN remains popular for its flexibility and extensive platform support.
Federal agencies have published guidance on modern network access security that emphasizes the transition from traditional VPN architectures to Zero Trust models. This shift reflects growing recognition that perimeter-based security no longer adequately protects against sophisticated threat actors.
| Protocol | Encryption | Performance | Use Case |
|---|---|---|---|
| WireGuard | ChaCha20 | Excellent | Modern deployments, mobile users |
| OpenVPN | AES-256-GCM | Good | Enterprise compatibility, legacy support |
| IKEv2/IPsec | AES-256 | Very Good | Mobile roaming, connection stability |
Beyond protocol selection, proper configuration is essential. This includes implementing strong cipher suites, enforcing certificate-based authentication rather than relying solely on passwords, and regularly updating VPN software to patch security vulnerabilities.
Authentication and Access Control
Effective vpn access remote security extends beyond encryption to encompass robust authentication mechanisms. Multi-factor authentication (MFA) has become a baseline requirement, adding critical protection against credential compromise. When passwords are stolen through phishing attacks or data breaches, MFA provides a crucial second layer of defense.
Modern implementations integrate identity providers using standards like SAML or OAuth, allowing organizations to centralize authentication and enforce consistent policies across all remote access points. Microsoft's guidance for securing VPN gateway deployments demonstrates how cloud identity platforms can enhance traditional VPN security through conditional access policies that evaluate device compliance, user location, and risk signals before granting access.
Implementing Least Privilege Access
Organizations should apply principle of least privilege when configuring vpn access remote permissions. Rather than granting full network access to all authenticated users, segment resources and limit each user to only the systems and data required for their specific role.
This approach reduces the potential damage from compromised credentials or insider threats. If an attacker gains access to one set of VPN credentials, proper segmentation prevents lateral movement across the entire network.
- Implement network segmentation using VLANs or software-defined perimeters
- Deploy jump servers or privileged access workstations for administrative functions
- Use application-specific access controls rather than broad network permissions
- Regularly audit and review access privileges to remove unnecessary permissions
- Monitor user behavior for anomalous activity that might indicate compromised credentials
European cybersecurity authorities have published technical guidance on remote identity proofing that addresses MFA implementation, identity verification, and regulatory compliance considerations particularly relevant for organizations operating under NIS2 and GDPR requirements.
Performance Optimization for Remote Workers
While security remains paramount, vpn access remote solutions must also deliver acceptable performance to support productivity. Remote workers accessing cloud applications, video conferencing systems, and large file repositories need sufficient bandwidth and low latency to work effectively.
Several factors influence VPN performance: encryption overhead, server capacity and location, network routing efficiency, and protocol optimization. Organizations with global workforces should deploy geographically distributed VPN endpoints to minimize latency for users in different regions.
Split Tunneling Considerations
Split tunneling allows vpn access remote clients to route some traffic through the encrypted tunnel while sending other traffic directly to the internet. This approach can significantly improve performance by reducing load on VPN infrastructure and eliminating unnecessary encryption overhead for trusted services.
However, split tunneling introduces security considerations. Organizations must carefully define which applications and destinations warrant direct internet access versus encrypted tunnel routing. Sensitive business applications and internal resources should always traverse the VPN, while general internet browsing might safely use direct connections.
For organizations seeking the best possible performance, providers like ZioFree maintain high-speed global server networks specifically optimized for minimal latency and maximum throughput, ensuring that security doesn't come at the cost of user experience.
Operational Technology and Industrial Remote Access
Beyond traditional office environments, vpn access remote solutions play critical roles in industrial control systems, manufacturing facilities, and critical infrastructure operations. These operational technology (OT) environments present unique security challenges that require specialized approaches.
NIST has published comprehensive guidance on OT security that addresses secure remote access for industrial control systems. These environments often involve legacy systems that cannot be easily updated, long-lived connections that must remain stable for continuous operations, and safety-critical processes where security measures cannot interfere with operational requirements.
Securing Critical Infrastructure Access
Industrial remote access requires additional safeguards:
- Network segmentation isolating OT systems from corporate IT networks
- Dedicated VPN infrastructure exclusively for industrial remote access
- Change control processes requiring approval for remote configuration changes
- Session monitoring and recording for audit and forensic purposes
- Fail-safe mechanisms ensuring operational continuity if VPN fails
The SANS Institute provides practical guidance on securing remote access for OT environments, emphasizing defense-in-depth strategies that combine network controls, endpoint security, and operational procedures.
Privacy Considerations and VPN Limitations
While vpn access remote solutions provide essential security benefits, users should understand their privacy implications and technical limitations. Research on VPN fingerprinting and privacy issues reveals that some VPN implementations may inadvertently leak identifying information through protocol characteristics, traffic patterns, or DNS queries.
Organizations committed to protecting user privacy should implement no-logs policies that prevent retention of connection metadata, browsing history, or traffic content. However, operational requirements for security monitoring and incident response may necessitate some level of logging, creating tensions between privacy and security objectives.
DNS Leaks and IPv6 Considerations
Common vpn access remote vulnerabilities include DNS leaks, where domain name resolution requests bypass the encrypted tunnel and expose browsing activity to internet service providers or network observers. Proper VPN configuration should force all DNS queries through the tunnel or use encrypted DNS protocols like DNS-over-HTTPS.
IPv6 presents another challenge, as some VPN clients fail to properly route IPv6 traffic through encrypted tunnels. Organizations should either ensure complete IPv6 support throughout their VPN infrastructure or disable IPv6 on client devices to prevent leakage.
Moving Toward Zero Trust Architecture
Traditional vpn access remote models assume that authenticated users connecting through encrypted tunnels should be trusted with broad network access. Zero Trust architecture challenges this assumption, requiring continuous verification and least-privilege access regardless of network location.
Google's BeyondCorp framework demonstrates how application-specific access controls can replace traditional network-level VPNs. Rather than granting access to entire network segments, Zero Trust models authenticate users and devices for each specific application or resource, continuously evaluating trust based on multiple signals.
Implementing Hybrid Approaches
Most organizations cannot immediately abandon existing vpn access remote infrastructure in favor of pure Zero Trust models. Instead, hybrid approaches combine traditional VPNs with modern access controls:
- Deploy identity-aware proxies in front of critical applications
- Implement device compliance checking before granting VPN access
- Use micro-segmentation within VPN-accessible networks
- Gradually migrate applications to cloud-based access models
- Maintain VPNs for legacy systems requiring network-level connectivity
Cloudflare's Zero Trust documentation describes clientless browser isolation and other alternatives that reduce reliance on full-network VPN access while maintaining security for web-based applications.
Hardening VPN Infrastructure
VPN gateways themselves represent high-value targets for attackers seeking network access. Proper hardening of this infrastructure is essential for maintaining overall security posture. CISA's hardening guidance for communications infrastructure provides technical recommendations specifically addressing VPN gateway exposure and configuration security.
Essential Hardening Measures
Organizations should implement comprehensive hardening for vpn access remote infrastructure:
| Category | Hardening Measure | Impact |
|---|---|---|
| Exposure | Minimize public-facing ports | Reduces attack surface |
| Authentication | Require certificate + MFA | Prevents credential attacks |
| Patching | Automated update deployment | Eliminates known vulnerabilities |
| Monitoring | Real-time intrusion detection | Enables rapid incident response |
| Configuration | Disable legacy protocols | Prevents downgrade attacks |
Regular vulnerability assessments and penetration testing should specifically target VPN infrastructure to identify weaknesses before attackers exploit them. Given the critical role these systems play in remote access, organizations should prioritize rapid patching of VPN software when security updates become available.
Mobile Device Management Integration
As remote work increasingly occurs on mobile devices, vpn access remote solutions must integrate with mobile device management (MDM) platforms. This integration enables enforcement of security policies on smartphones and tablets accessing corporate resources.
MDM platforms can verify device compliance before allowing VPN connections, checking for required security updates, encryption status, and absence of jailbreaking or rooting. Non-compliant devices can be blocked from accessing sensitive resources until they meet security requirements.
Organizations should configure per-app VPN capabilities available on modern mobile platforms, routing only specific business applications through the VPN tunnel while allowing personal apps to access the internet directly. This approach balances security with user privacy on employee-owned devices.
Cost Considerations and Vendor Selection
Implementing robust vpn access remote infrastructure requires careful evaluation of costs beyond initial licensing fees. Organizations should consider total cost of ownership including infrastructure hardware, bandwidth requirements, administrative overhead, and support resources.
For smaller organizations or those seeking to minimize infrastructure management, cloud-based VPN services offer attractive alternatives to on-premises deployments. These managed solutions provide geographic distribution, automatic scaling, and reduced operational complexity at predictable monthly costs.
When evaluating providers, examine their security features, encryption standards, server locations, connection speeds, and privacy policies. Organizations with specific compliance requirements should verify that potential vendors can meet regulatory obligations for data protection and logging.
Training and User Adoption
Even the most sophisticated vpn access remote technology fails if users don't properly adopt it. Organizations should invest in training programs that help remote workers understand:
- How to connect to the VPN from different locations and devices
- When VPN usage is required versus optional
- How to recognize and report connection problems
- Security best practices for remote work environments
- Troubleshooting common issues without requiring IT support
User-friendly client software with minimal configuration requirements improves adoption rates and reduces support burden. Automated connection features that establish VPN tunnels when accessing corporate resources eliminate the need for users to remember manual connection procedures.
Regular communications about security threats and best practices keep remote access security top of mind. Organizations should share examples of real-world attacks targeting remote workers to illustrate the importance of following security protocols.
Monitoring and Incident Response
Comprehensive monitoring of vpn access remote infrastructure provides visibility into potential security incidents and performance issues. Organizations should collect and analyze logs from VPN gateways, authentication servers, and client devices to detect anomalous behavior.
Key metrics and events to monitor include:
- Failed authentication attempts that might indicate credential guessing attacks
- Connections from unusual geographic locations or suspicious IP addresses
- Abnormal data transfer volumes suggesting data exfiltration
- Multiple simultaneous connections from a single user account
- Connection attempts using deprecated protocols or weak encryption
Security information and event management (SIEM) systems can correlate VPN logs with other security data to identify sophisticated attacks that might not be apparent from VPN logs alone. Automated alerting ensures that security teams receive timely notification of potential incidents requiring investigation.
Securing remote access in 2026 requires balancing robust security controls with user experience and operational efficiency. Organizations must carefully select appropriate protocols, implement strong authentication, maintain infrastructure security, and continuously adapt to evolving threats. ZioFree delivers enterprise-grade VPN access remote capabilities with military-level encryption, a global server network optimized for speed, and a strict no-logs policy that protects your privacy while defending against sophisticated threats. Secure your distributed workforce today with a trusted solution built for the modern threat landscape.